
By Tech & Security Desk
Published: October
Main Facts: Opening the Doors to Advanced AI Cybersecurity
In a significant policy shift aimed at bolstering the global cybersecurity defense community, Anthropic has officially expanded its cybersecurity verification program. Announced on October 6, the updated framework integrates the previously exclusive Project Glasswing into a broader, more structured tiered access system. This strategic evolution is designed to grant legitimate security professionals, researchers, and software maintainers deeper, more uninhibited access to Anthropic’s advanced Claude model family while maintaining stringent guardrails against malicious exploitation.
The expanded initiative opens the door not only to large enterprise security operations centers (SOCs) but also to smaller teams, open-source software maintainers, and individual security researchers who possess a verifiable track record of responsible vulnerability disclosure. However, Anthropic is careful to clarify that "fewer blocks" does not equate to a free-for-all. The platform continues to enforce rigorous verification protocols, multi-factor identity checks, continuous monitoring, and strict authorization requirements regarding the specific environments in which the models are deployed.
At the heart of this expansion is access to Anthropic’s cutting-edge model lineup, including Claude Opus 5.5, Sonnet 5.5, and Mythos 5.1, alongside provisions for future generations of models. While previous announcements—such as the debut of Opus 5.5—focused primarily on cost-efficiency and computational performance, this latest update fundamentally redefines who is permitted to wield these potent capabilities and under what precise operational parameters.
The models are now accessible across major cloud ecosystems, including the Claude Platform, Google Cloud’s Vertex AI, and Microsoft Foundry. Availability on Amazon Bedrock, meanwhile, is currently restricted to customers who qualify for forthcoming specialized deployment configurations.
Chronology: The Evolution of Project Glasswing and Anthropic’s Security Policy
To understand the weight of Anthropic’s October 6 announcement, it is essential to trace the trajectory of how the artificial intelligence industry—and Anthropic in particular—has handled dual-use cybersecurity capabilities.
- Early Generative AI Era: Initially, leading foundational models were heavily sandboxed. Safety filters routinely flagged and blocked security-related queries, frustrating defenders who sought to use AI for malware analysis, threat hunting, and reverse engineering, out of fear that the models could be co-opted to write exploits.
- The Inception of Project Glasswing: Recognizing that malicious actors were already adopting AI while legitimate defenders were handcuffed by over-cautious safety classifiers, Anthropic launched Project Glasswing. This initiative served as a tightly controlled, highly vetted sandbox for select researchers to test advanced AI models against sophisticated cyber threats.
- Late 2024 to Mid-2025 (Model Advancements): Anthropic rolled out increasingly capable iterations of its models, such as the Opus and Mythos families. Discussions around pricing, efficiency, and architectural scaling—such as the 40% cost reduction seen in Opus 5.5—dominated tech circles, but the bottleneck remained: access to offensive and advanced defensive workflows was bottlenecked by manual, slow onboarding.
- October 6, 2025 (The Expansion): Anthropic dismantled the single-tier bottleneck of Glasswing, officially integrating it into a comprehensive, three-tiered verification program. This move democratized access for smaller entities, independent researchers, and open-source maintainers, establishing a scalable framework for vetting and authorizing AI-driven security work.
Supporting Data: The Three-Tiered Access Architecture and Internal Evaluations
The newly structured program breaks down the authorization process into three distinct operational tiers, each tailored to specific risk profiles and technical requirements.
+-------------------------------------------------------------------+
                  ANTHROPIC CYBERSECURITY TIERS
+-------------------------------------------------------------------+
  [Tier 1: Defense Access]
  -> Focus: Threat hunting, malware analysis, incident response.
  -> Eligibility: Broad (Companies, Universities, NGOs, Hospitals).

  [Tier 2: Red Team Access]
  -> Focus: Authorized penetration testing & offensive simulation.
  -> Eligibility: Organizations only (No individual researchers).

  [Tier 3: Specialized Access]
  -> Focus: Critical infrastructure (Grids, Aviation, Banking).
  -> Eligibility: Highly vetted entities, US Gov coordination.
+-------------------------------------------------------------------+
1. Defense Access (Defensive Operations)
This foundational tier covers standard security operations, incident response protocols, malware reverse-engineering, and vulnerability validation.
- Eligible Entities: Commercial enterprises, academic institutions, non-profit organizations, public sector entities, and regional critical infrastructure operators (such as regional hospitals and municipal utilities).
- Onboarding: Anthropic aims to process these applications within a matter of days, though approval is evaluated on a case-by-case basis.
2. Red Team Access (Authorized Offensive Testing)
Stepping into the offensive domain, this tier permits penetration testing, red-teaming exercises, and security simulations, provided they are executed strictly against systems for which the operating entity holds explicit legal authorization.
- Eligible Entities: Strictly reserved for corporate and institutional organizations; individual researchers are barred from this tier.
- Review Process: Due to the inherent risks associated with offensive capabilities, vetting can take several weeks. However, organizations undergoing review may be granted temporary access to the defensive tier while their application is processed.
- Hard Boundaries: Even within this advanced tier, immutable safety locks remain active to prevent actions that could cause catastrophic physical damage or mass disruptions—such as the automated large-scale deployment of ransomware or unauthorized probing of high-risk national security infrastructure.
3. Specialized Access (Critical Systems and National Security)
Reserved for an elite, highly vetted group of organizations stress-testing systems where failures could result in immediate loss of life or systemic economic collapse.
- Scope: Encompasses national power grids, commercial aviation control systems, and core interbank financial transfer networks.
- Oversight: Anthropic has stated that these cases undergo rigorous joint reviews with the United States government. Current participants in the legacy Project Glasswing initiative are automatically grandfathered into this tier without needing to re-apply for currently active models.
Internal Efficacy Data
To illustrate the efficacy of these boundaries, Anthropic released internal evaluation metrics utilizing Claude Opus 5.5:
- Defense Access Tier: Under simulated offensive scenarios, this tier successfully intercepted and blocked 46 out of 50 malicious or high-risk prompts, proving that the defensive guardrails remain robust against accidental or intentional misuse.
- Red Team Access Tier: Under identical testing conditions, this authorized tier did not block the authorized testing prompts, successfully executing 34 out of 34 requested specialized tasks.
Note: Anthropic explicitly notes that these figures represent internal benchmarks rather than independent third-party audits or guaranteed success rates in live, unpredictable enterprise environments.
Official Responses and Strategic Rationale
The cybersecurity community has long grappled with the "dual-use dilemma" of artificial intelligence: tools capable of patching zero-day vulnerabilities can, by extension, be weaponized to discover them. Anthropic’s leadership has framed this policy expansion not as a loosening of safety standards, but as a maturation of risk management.
By moving away from a blanket prohibition—which often drove developers and researchers toward unmonitored open-source models with zero safety guardrails—Anthropic is attempting to capture the "defender’s advantage."
"We cannot secure the digital ecosystem by pretending that advanced reasoning models cannot be used for security analysis," noted a security policy briefing from the company. "By creating clear, verifiable pathways for defenders, we ensure that the good guys have access to the absolute best tools available, while retaining the technical telemetry necessary to detect, log, and neutralize bad actor attempts."
Data retention remains a cornerstone of this oversight model. To deter and investigate potential policy violations, Anthropic mandates telemetry and prompt logging for standard program participants. However, acknowledging enterprise concerns regarding corporate privacy and intellectual property, the company provides exceptions for organizations operating under zero-retention agreements using models like Fable 5.1 or Mythos 5.1. Furthermore, Anthropic is actively developing Enterprise Frontier Safeguards, a forthcoming architectural solution designed to allow eligible enterprises to process and store their security data entirely within their own private, sovereign infrastructure.
Implications for the Cybersecurity Landscape
The expansion of Anthropic’s verification program carries profound ramifications for the broader technology and security sectors.
1. Empowering the Under-Resourced Defender
Historically, advanced AI-driven security tooling has been the exclusive domain of nation-states and Fortune 500 enterprises with massive compliance budgets. By opening Defense Access to open-source software maintainers, independent researchers, and regional entities (like local healthcare providers), Anthropic is leveling the playing field. Critical open-source libraries—which form the invisible infrastructure of the modern web—can now be audited and patched with the speed and scale that AI affords.
2. Redefining "Vibe Coding" and Software Security
As AI rapidly changes the rules of application development through paradigm shifts like "vibe coding"—where developers build complex applications via natural language prompts—the surface area for software vulnerabilities has expanded exponentially. When anyone can spin up a complex codebase in minutes, the need for automated, AI-assisted code review and rapid vulnerability identification becomes paramount. Anthropic’s tiered approach ensures that developers building next-generation software have immediate access to defensive auditing tools without bypassing necessary legal and operational checks.
3. The Compliance and Liability Conundrum
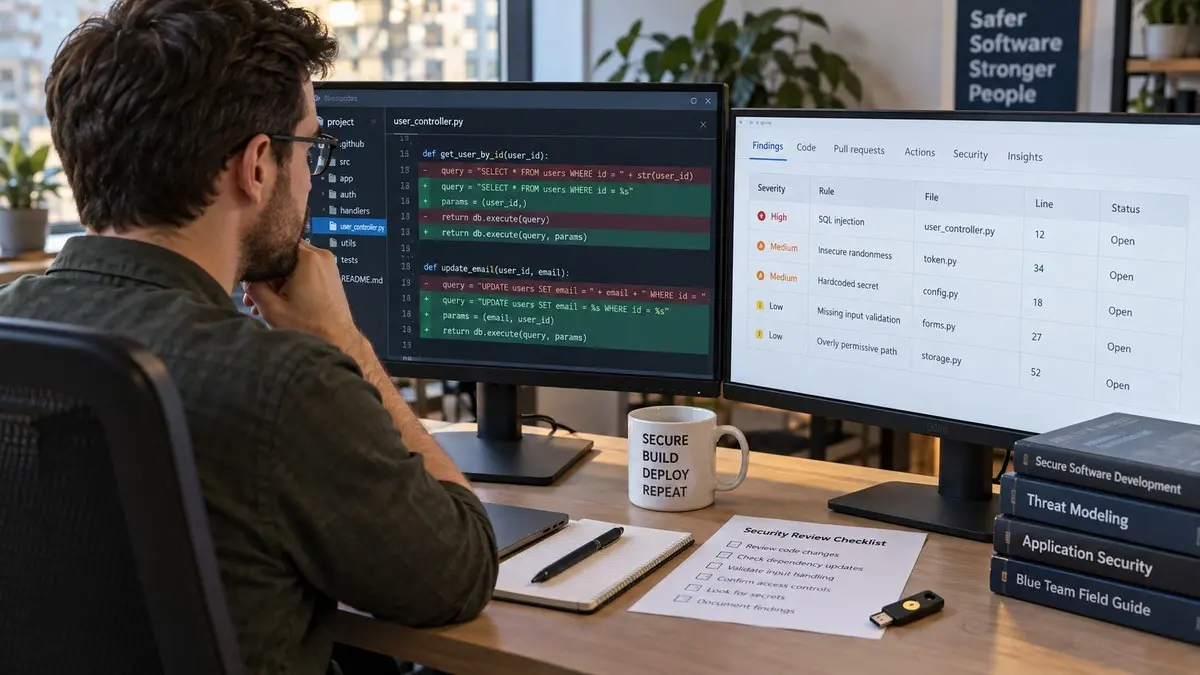
For organizations seeking Red Team or Specialized Access, the hurdle is no longer just technical; it is regulatory and legal. Requiring explicit authorization for penetration testing means that corporate legal teams must tightly integrate with engineering departments before querying Claude. This creates a formalized paper trail, reducing the gray areas of ethical hacking and establishing clearer legal accountability for AI-assisted security operations.
4. Setting the Industry Standard
As Google, OpenAI, and other foundational model providers watch this rollout, Anthropic’s three-tiered model may well become the baseline compliance framework for the entire generative AI industry. Balancing open access for vetted defenders with hard-coded boundaries against mass-disruption threats offers a viable blueprint for how powerful cognitive technologies can be safely integrated into high-stakes environments.
Ultimately, Anthropic’s October 6 announcement signals a pragmatic maturity in AI governance: the recognition that safety is not achieved by locking tools away in a vault, but by building secure, verifiable bridges between the artificial intelligence models of tomorrow and the human defenders protecting the digital world today.

Leave a Reply