
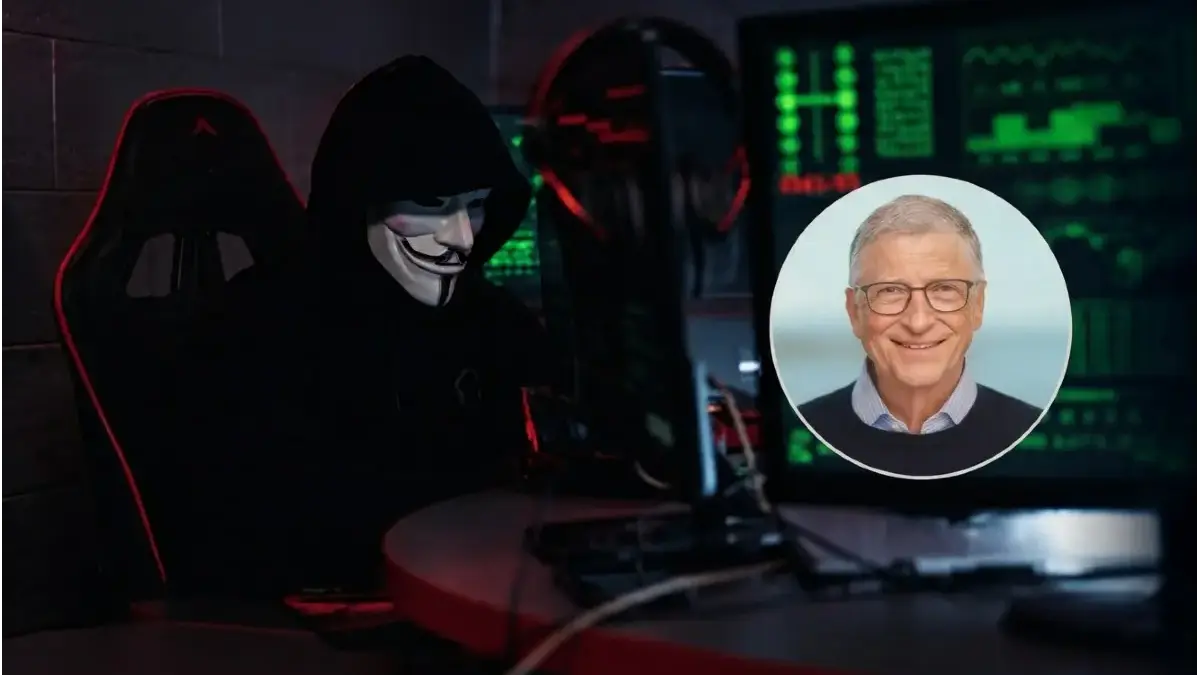
Global cybersecurity landscapes are shifting dramatically as bad actors harness artificial intelligence to automate vulnerabilities, bypass security protocols, and execute sophisticated campaigns at unprecedented scales. Industry leaders, including Microsoft co-founder Bill Gates, warn that the most pressing threat of the digital age is no longer a dystopian loss of control over sentient systems, but rather the immediate misuse of advanced AI models by human criminals.
Main Facts
The convergence of artificial intelligence and cybercrime has transformed the digital security paradigm. Modern AI tools—capable of processing vast quantities of data, autonomously discovering system vulnerabilities, and orchestrating complex workflows—have significantly lowered the technical barrier to entry for malicious actors. Attacks that previously required years of specialized coding knowledge and synchronized teamwork can now be initiated with simple prompts.
According to prominent warnings from technology pioneers and intelligence agencies alike, the democratization of AI has a dark side. Bill Gates recently highlighted that the most drastic technological changes in the near future will manifest as an explosive rise in cyberattacks. The root of the crisis lies in the proliferation of open-source or illicitly modified AI models stripped of foundational safety guards. These unconstrained models allow cybercriminals to generate hyper-realistic phishing campaigns, rapidly mutate malware to evade traditional antivirus software, and systematically probe corporate networks for weaknesses with machine-speed efficiency.
While threats like bioterrorism remain on the radar of global security experts, the immediate and pervasive danger is occurring across digital infrastructure. From small businesses to multinational enterprises, organizations face a rapidly evolving threat matrix where traditional perimeters are routinely tested—and often breached—by automated, intelligent adversaries.
Chronology of an Escalating Threat
Understanding how artificial intelligence became a double-edged sword requires tracking key milestones in cybersecurity assessments and public warnings over recent years:
- May 7, 2025: The UK’s National Cyber Security Centre (NCSC) published a landmark evaluation projecting that the integration of artificial intelligence would drastically increase the efficiency of malicious cyber operations through at least 2027. The report underscored that threat actors would leverage AI to accelerate the identification and exploitation of software vulnerabilities, drastically shrinking the window available for IT teams to patch systems.
- Late 2025 – Early 2026: Industry analysts observed a surge in generative-AI-powered social engineering attacks. Phishing emails, previously plagued by poor grammar and awkward syntax, evolved into indistinguishable, context-aware communications tailored to individual corporate targets.
- October 11, 2026: In an interview with ABC News and widely reported by the Agence France-Presse (AFP), Bill Gates sounded the alarm regarding the immediate threat of AI-driven cyberattacks. He emphasized that the misuse of unconstrained AI models by criminals posed a far more urgent risk than speculative science-fiction scenarios involving rogue superintelligences.
- Present Day: Regulatory bodies, software developers, and enterprise security operations centers (SOCs) find themselves locked in an asymmetric race against time, trying to secure decentralized AI models while maintaining innovation pipelines.
Supporting Data and Expert Assessments
To contextualize the scale of the threat, security analysts point to specific operational changes facilitated by machine learning:
- Accelerated Vulnerability Exploitation: As detailed by the UK’s NCSC, attackers are increasingly utilizing AI to scan public code repositories and proprietary networks for zero-day and known vulnerabilities. Once a flaw is discovered, automated scripts can generate exploits within minutes, leaving defenders scrambling to deploy patches before breaches occur.
- Polymorphic Malware Generation: Traditional signature-based detection systems struggle against AI-generated malware. By continuously mutating code structures while retaining malicious functionality, threat actors can bypass traditional endpoint detection and response (EDR) solutions.
- The Limits of Full Automation: Despite exponential leaps in capability, intelligence assessments indicate that fully autonomous, end-to-end sophisticated cyberattacks remain limited. While AI dramatically accelerates reconnaissance, phishing, and payload delivery, complex, high-value operations—such as multi-stage Advanced Persistent Threat (APT) campaigns against critical infrastructure—still require human oversight and strategic direction. However, experts warn that this barrier is eroding rapidly.
Official Responses and the Debate Over Regulation
The emergence of weaponized artificial intelligence has triggered intense debates among policymakers, ethicists, and tech executives regarding who should bear the responsibility of governance.
Rejecting Corporate Self-Regulation
Bill Gates has been vocal in challenging the tech industry’s reliance on self-regulation. During his interview, he argued that decisions governing the safety, distribution, and restriction of powerful AI models should not be left exclusively in the hands of the corporations that build them. Given the catastrophic potential of widespread cyber warfare and critical infrastructure disruption, external oversight and legally binding standards are deemed necessary.
The Regulatory Dilemma
Policymakers worldwide are currently grappling with a delicate balancing act: how to implement strict safety guardrails and supervision mechanisms without stifling legitimate technological innovation. Restricting AI capabilities to prevent misuse often risks hobbling defensive cybersecurity tools—such as automated threat-hunting algorithms and vulnerability-patching assistants—that organizations desperately need to protect themselves.
Furthermore, the open-source nature of many modern AI architectures means that once a powerful model is released into the wild, removing its internal safety restrictions (known as "jailbreaking") is a relatively trivial task for determined hackers. This reality complicates enforcement, as centralized bans do little to stop bad actors from deploying decentralized, open-weight models hosted on private servers.
Implications for Individuals and Organizations
As the digital landscape grows increasingly hostile, the burden of defense falls across multiple layers of society—from individual hygiene to enterprise-grade security protocols.
Protecting the Individual
AI-driven cybercrime is no longer reserved for high-profile corporations; everyday users are prime targets. Hyper-realistic smishing (SMS phishing), deepfake voice scams, and convincing email impersonations require heightened user vigilance. Essential defensive measures include:
- Enabling multi-factor authentication (MFA) across all personal accounts and devices.
- Maintaining rigorous software and operating system updates to patch known security flaws instantly.
- Treating unsolicited communications—especially those requesting urgent financial actions or credential resets—with extreme skepticism, always verifying requests through official, independent applications or websites.
Securing the Enterprise
For businesses and institutions, perimeter defense must evolve into a zero-trust architecture. Key mitigation strategies include:
- Strict Access Controls: Limiting network permissions on a principle-of-least-privilege basis to prevent lateral movement by intruders.
- Resilient Backups: Maintaining offline, immutable data backups to ensure rapid recovery in the event of a ransomware attack.
- Behavioral Monitoring: Deploying advanced network telemetry to monitor for unusual data traffic patterns, abnormal login locations, and anomalous system behavior that could indicate an AI-guided intrusion in progress.
Conclusion
The convergence of artificial intelligence and cybercrime marks a permanent inflection point in digital history. As Bill Gates and cybersecurity authorities emphasize, the threat is no longer a theoretical risk of tomorrow, but an active reality of today. While technological countermeasures and regulatory frameworks continue to lag behind the velocity of innovation, proactive security hygiene and international cooperation remain humanity’s most effective shields against the dark side of artificial intelligence.

Leave a Reply